
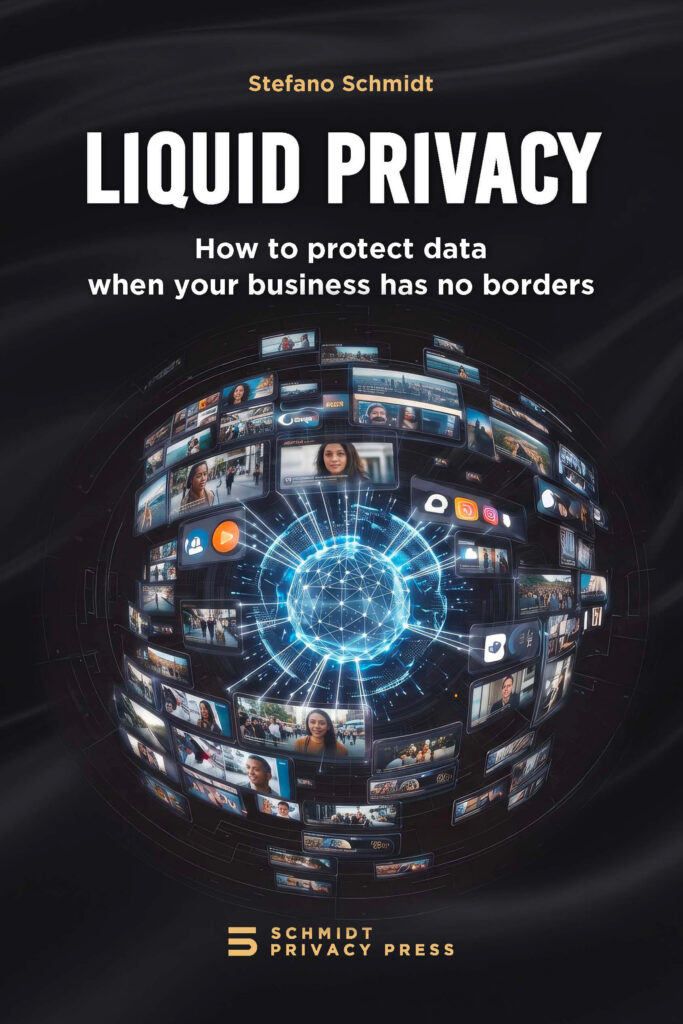
The book
More and more businesses are liquid: organisations with no traditional premises, running on a laptop, an internet connection and a cloud database. The pandemic sped up a change that was already under way. Businesses became lighter, faster and freer to adapt to the market, but they also opened up new vulnerabilities.
The GDPR was designed with a “solid” business in mind: a head office, in-house servers, archives behind a locked door. Today that door no longer exists. Data moves between public clouds, SaaS platforms, personal drives and smartphones. The workforce is a mix of employees, freelancers and consultants in different cities and countries. The company perimeter has dissolved.
Yet many businesses still handle privacy as if nothing had changed: a privacy notice copied from the internet, a consent box ticked on a form, an Excel file of appointments. Liquid Privacy shows how to cross the “liminal space” between those who are at the mercy of privacy and those who govern it: from chaos to compliance, from compliance to governance, and finally to turning data protection into a source of trust and competitive advantage.
It is a practical book, built on years of audits and consultancy work with start-ups, digital companies, professional networks and service firms. It is full of real cases, examples and tools you can use straight away.
Who it is for
- Entrepreneurs and managers of start-ups, scale-ups and digital companies
- Organisations that work remotely, in hybrid mode or with many external collaborators
- IT, HR and operations managers who run cloud tools and access rights
- DPOs and consultants who support fluid organisations
What you will find in the book
- What it means to be a liquid business, and why the traditional perimeter is no longer enough
- The three stages of privacy maturity: chaos, compliance, governance
- Why “just get consent” is not enough, and how to choose the right lawful basis
- Collaborators, authorised persons or processors: who is who, and how to build a chain of trust
- When you need a DPO and when you have to carry out a data protection impact assessment (DPIA)
- How to prepare for a GDPR audit
- Cybersecurity and the cloud: the new perimeter of the digital business
- Governance and accountability: from paperwork to culture